
Information Security
Information Security Management Policy
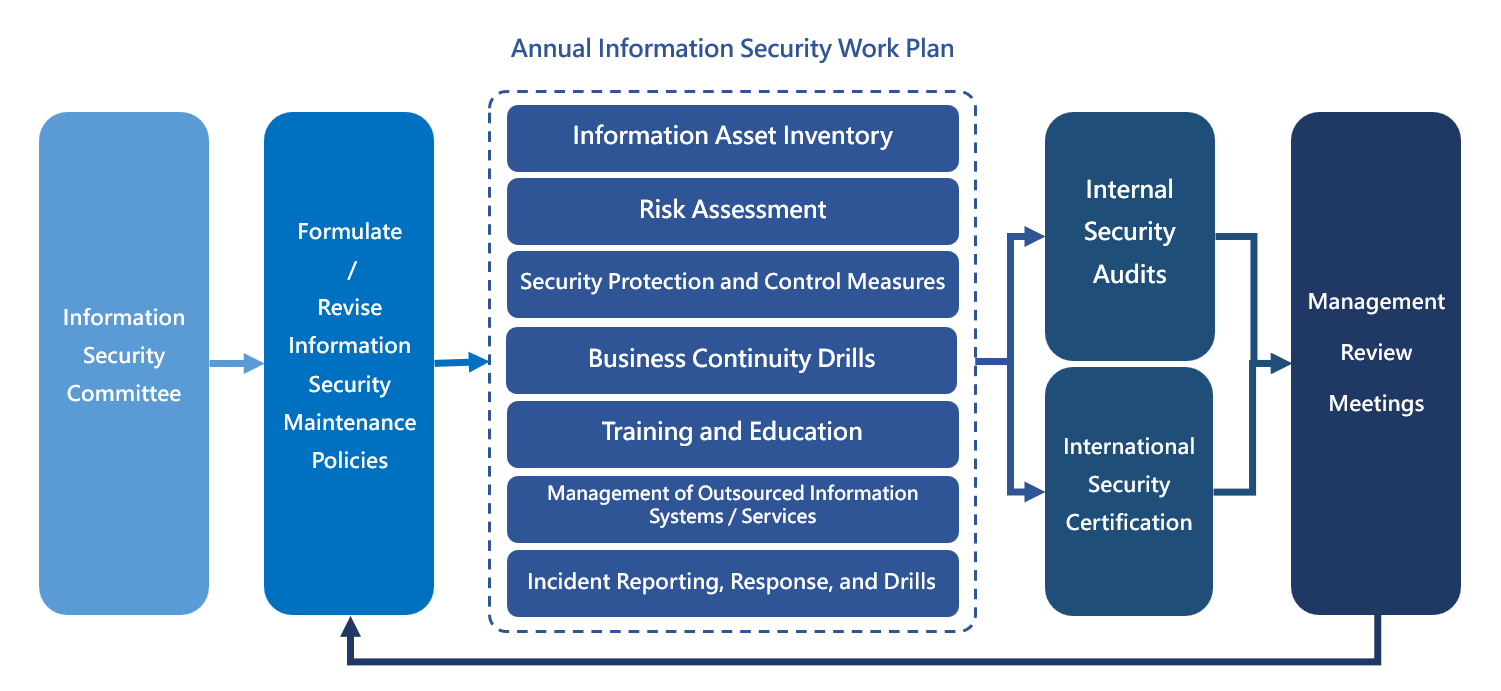
To safeguard data, systems, equipment, and networks, the University implements its Information and Communication Security Policy and Information Security Management System (ISMS).
The Information Security Management Committee annually reviews security performance, stakeholder feedback, emerging issues, and risk assessments to ensure policy effectiveness.
|
Develop Smart Campus Administration System |
Build Smart Campus Administration System |
Develop a high-quality, non-quantitative smart campus administration system based on the needs of all administrative and academic units. |
|
Expand System Functions |
Gradually expand and add functions to existing systems to meet regulations, align with administrative processes, and improve efficiency. |
|
|
Upgrade Systems for Higher Performance |
Upgrade and revamp systems, adopting mainstream application technologies to enhance development and maintenance performance. |
|
|
Enhance System Security |
Follow information security standards, improving systems annually through vulnerability scanning and penetration testing to strengthen overall security. |
|
|
Strengthen Campus Information Infrastructure |
Establish High-Speed Campus Network |
Continuously replace outdated network equipment, wiring, and wireless infrastructure, while enhancing data center operations management. |
|
Create Advanced Computing Environment |
Expand virtual platforms for teaching, research, and projects, as well as the CSU Cloud Desktop, and promote the use of public cloud services. |
Information Security Awareness Platform

Information Security Management System Implementation Flowchart
Information Security Incident Management and Actions
Suspected cybersecurity incidents are assessed and reported under the Information Security Incident Management Procedures. in 2025, the University recorded three non-material incidents, none involving personally identifiable information.
The University strengthens cybersecurity through smart campus systems, upgraded IT infrastructure, vulnerability scanning, and penetration testing.
Information Security Training
The University regularly conducts training and internal and external audits to strengthen information security and personal data protection awareness. in 2025, the Office of Library and Information Services held eight training sessions, attracting 1,473 participants.
Personal Information Protection
To safeguard personal data, the University has issued a Privacy Protection Statement and established policies in compliance with applicable regulations.
The University operates a Personal Information Management System (PIMS) and a dedicated committee to oversee data protection. It obtained BS 10012 certification following an SGS audit in August 2024. No personal data breaches occurred in 2025.
◎ Key Controls for Personal Data Protection
|
● Ensure compliance with all applicable regulations on personal data protection. |
|
● Verify that the collection, processing, and use of personal data do not exceed the authorized scope. |
|
● Confirm that the personal data protection organization is established in accordance with regulations. |
|
● Review annually whether the retention of personal data files meets legal requirements; regularly update inventory accuracy and conduct risk assessments. |
|
● Ensure that cross-unit data transfers are reviewed and approved by authorized units, with records maintained. |
|
● Manage the collection, storage, and disposal of personal data in accordance with established procedures. |
|
● Safeguard the rights of data subjects as stipulated in the Data Subject Rights Management Regulations. |
|
●When outsourcing personal data processing, sign a written contract and comply with legal notification requirements for data collection and processing. |
|
●Implement emergency response measures in the event of a personal data security incident. |
Information Security and Personal Data Management System Certification
The University conducts regular third-party audits of its information security and personal data management systems to safeguard data confidentiality, availability, and integrity.
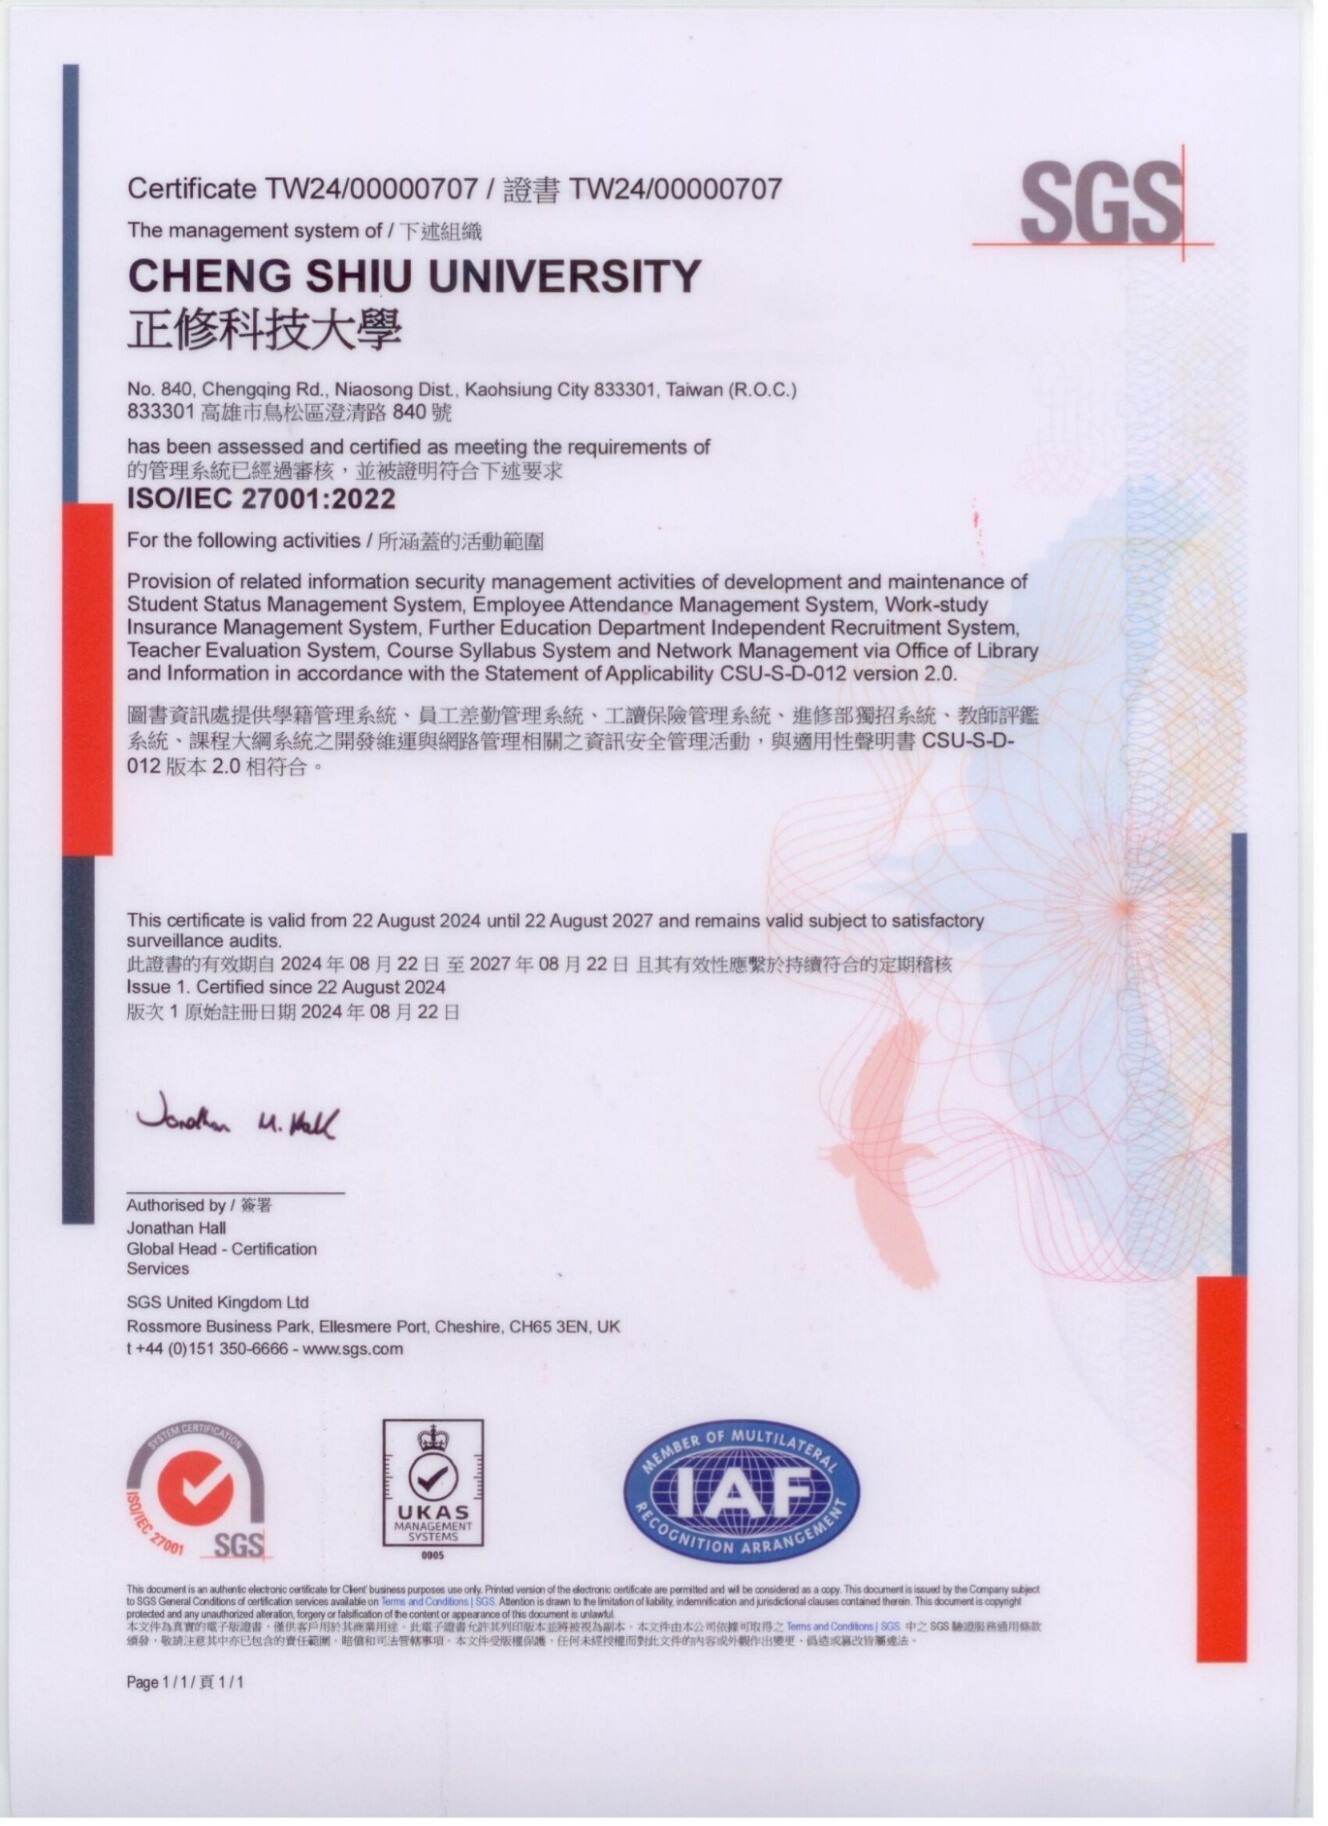
In 2025, six core administrative systems remained certified under ISO 27001:2022, with an external audit completed on June 30 to maintain certification validity.
For personal data management, external consultants supported system maintenance and internal audits covering four designated units in 2025. International certification for personal data management was discontinued in favor of consultant-assisted internal auditing.
|
ISO 27001 Information Security Management System (ISMS) Certification |
.2018: Obtained ISO 27001:2013 certification for student records, staff attendance, data center operations, and network infrastructure. .2021: Expanded the scope to include continuing education admissions and student worker insurance systems. .2023: Renewed certification for four core systems. .2024: Expanded certification to six core systems and obtained ISO 27001:2022 certification following an external audit in August. .2025: Renewed certification for all six core systems. |
|
BS 10012 Personal Information Management System (PIMS) Certification |
.2017: Implemented a University-wide Personal Information Management System (PIMS) and obtained BS 10012:2017 certification. .2020: Audited five units with high personal data risks. .2023: Expanded certification audits to six designated units and renewed certification. .2024: Conducted consultant-assisted internal audits of three units and continued related procedures. .2025: Conducted consultant-assisted internal audits of four units and maintained personal data protection procedures. |